VSAT GitHub

Audit the layer everything else runs on.

VSAT is a portable, read-only security assessment tool for the virtualization backbone of IT and OT networks. Run it on a connected network or carry it into an air-gapped enclave: one command, no agents, no internet, no telemetry, and an evidence-backed report you can open anywhere.

Downloads VSAT, checks it wasn't tampered with, then runs the safe built-in demo. Re-running the same line later updates to the newest release.

$u="https://github.com/NextSecurity/VSAT/releases/latest/download";iwr "$u/vsat.ps1" -OutFile vsat.ps1;iwr "$u/SHA256SUMS.txt" -OutFile SHA256SUMS.txt;$h=((gc SHA256SUMS.txt|?{$_ -match '\svsat\.ps1$'}) -split '\s+')[0];if((Get-FileHash vsat.ps1).Hash -ne $h){throw 'checksum mismatch - do not run'};Unblock-File vsat.ps1 -EA 0;./vsat.ps1 -Demo
Pin a version (reproducible)
$v='2.7.0';$u="https://github.com/NextSecurity/VSAT/releases/download/v$v";iwr "$u/vsat.ps1" -OutFile vsat.ps1;iwr "$u/SHA256SUMS.txt" -OutFile SHA256SUMS.txt;$h=((gc SHA256SUMS.txt|?{$_ -match '\svsat\.ps1$'}) -split '\s+')[0];if((Get-FileHash vsat.ps1).Hash -ne $h){throw 'checksum mismatch - do not run'};Unblock-File vsat.ps1 -EA 0;./vsat.ps1 -Demo

Real audit: ./vsat.ps1 opens the guided UI. Credentials are prompted, never typed on the command line.

The VSAT report's topology view in dark mode: a vCenter expands into a datacenter, two clusters and five ESXi hosts, each node outlined by its worst finding severity.
The topology view of the demo report, generated from the built-in synthetic example.local lab. Every screenshot on this page comes from that same file.

Built for security professionals

For teams that assess infrastructure they cannot expose or change, from enterprise datacenters to isolated defense, government and critical-infrastructure networks.

Penetration testers, red and blue teams
Attack paths, blast radius from a compromised account or VM, and an ATT&CK Navigator layer from one read-only run.
Assessors, auditors and MSSPs
Every finding carries observed and expected values, evidence, mitigation, rollback and validation. One report format across VMware, Hyper-V and KVM, with baselines that show drift between engagements.
Defense, government and OT/ICS teams
Runs inside air-gapped enclaves from a portable, hash-verified package. Installs nothing, sends nothing, never writes to the systems it audits.

One file you can carry out of the room

Every run writes a standalone report.html that works offline, next to an evidence package and CSV worklists. Twelve features go beyond a checklist, and each one says plainly how much it can tell you.

Findings, coverage and evidence confidence, kept as three separate numbers.

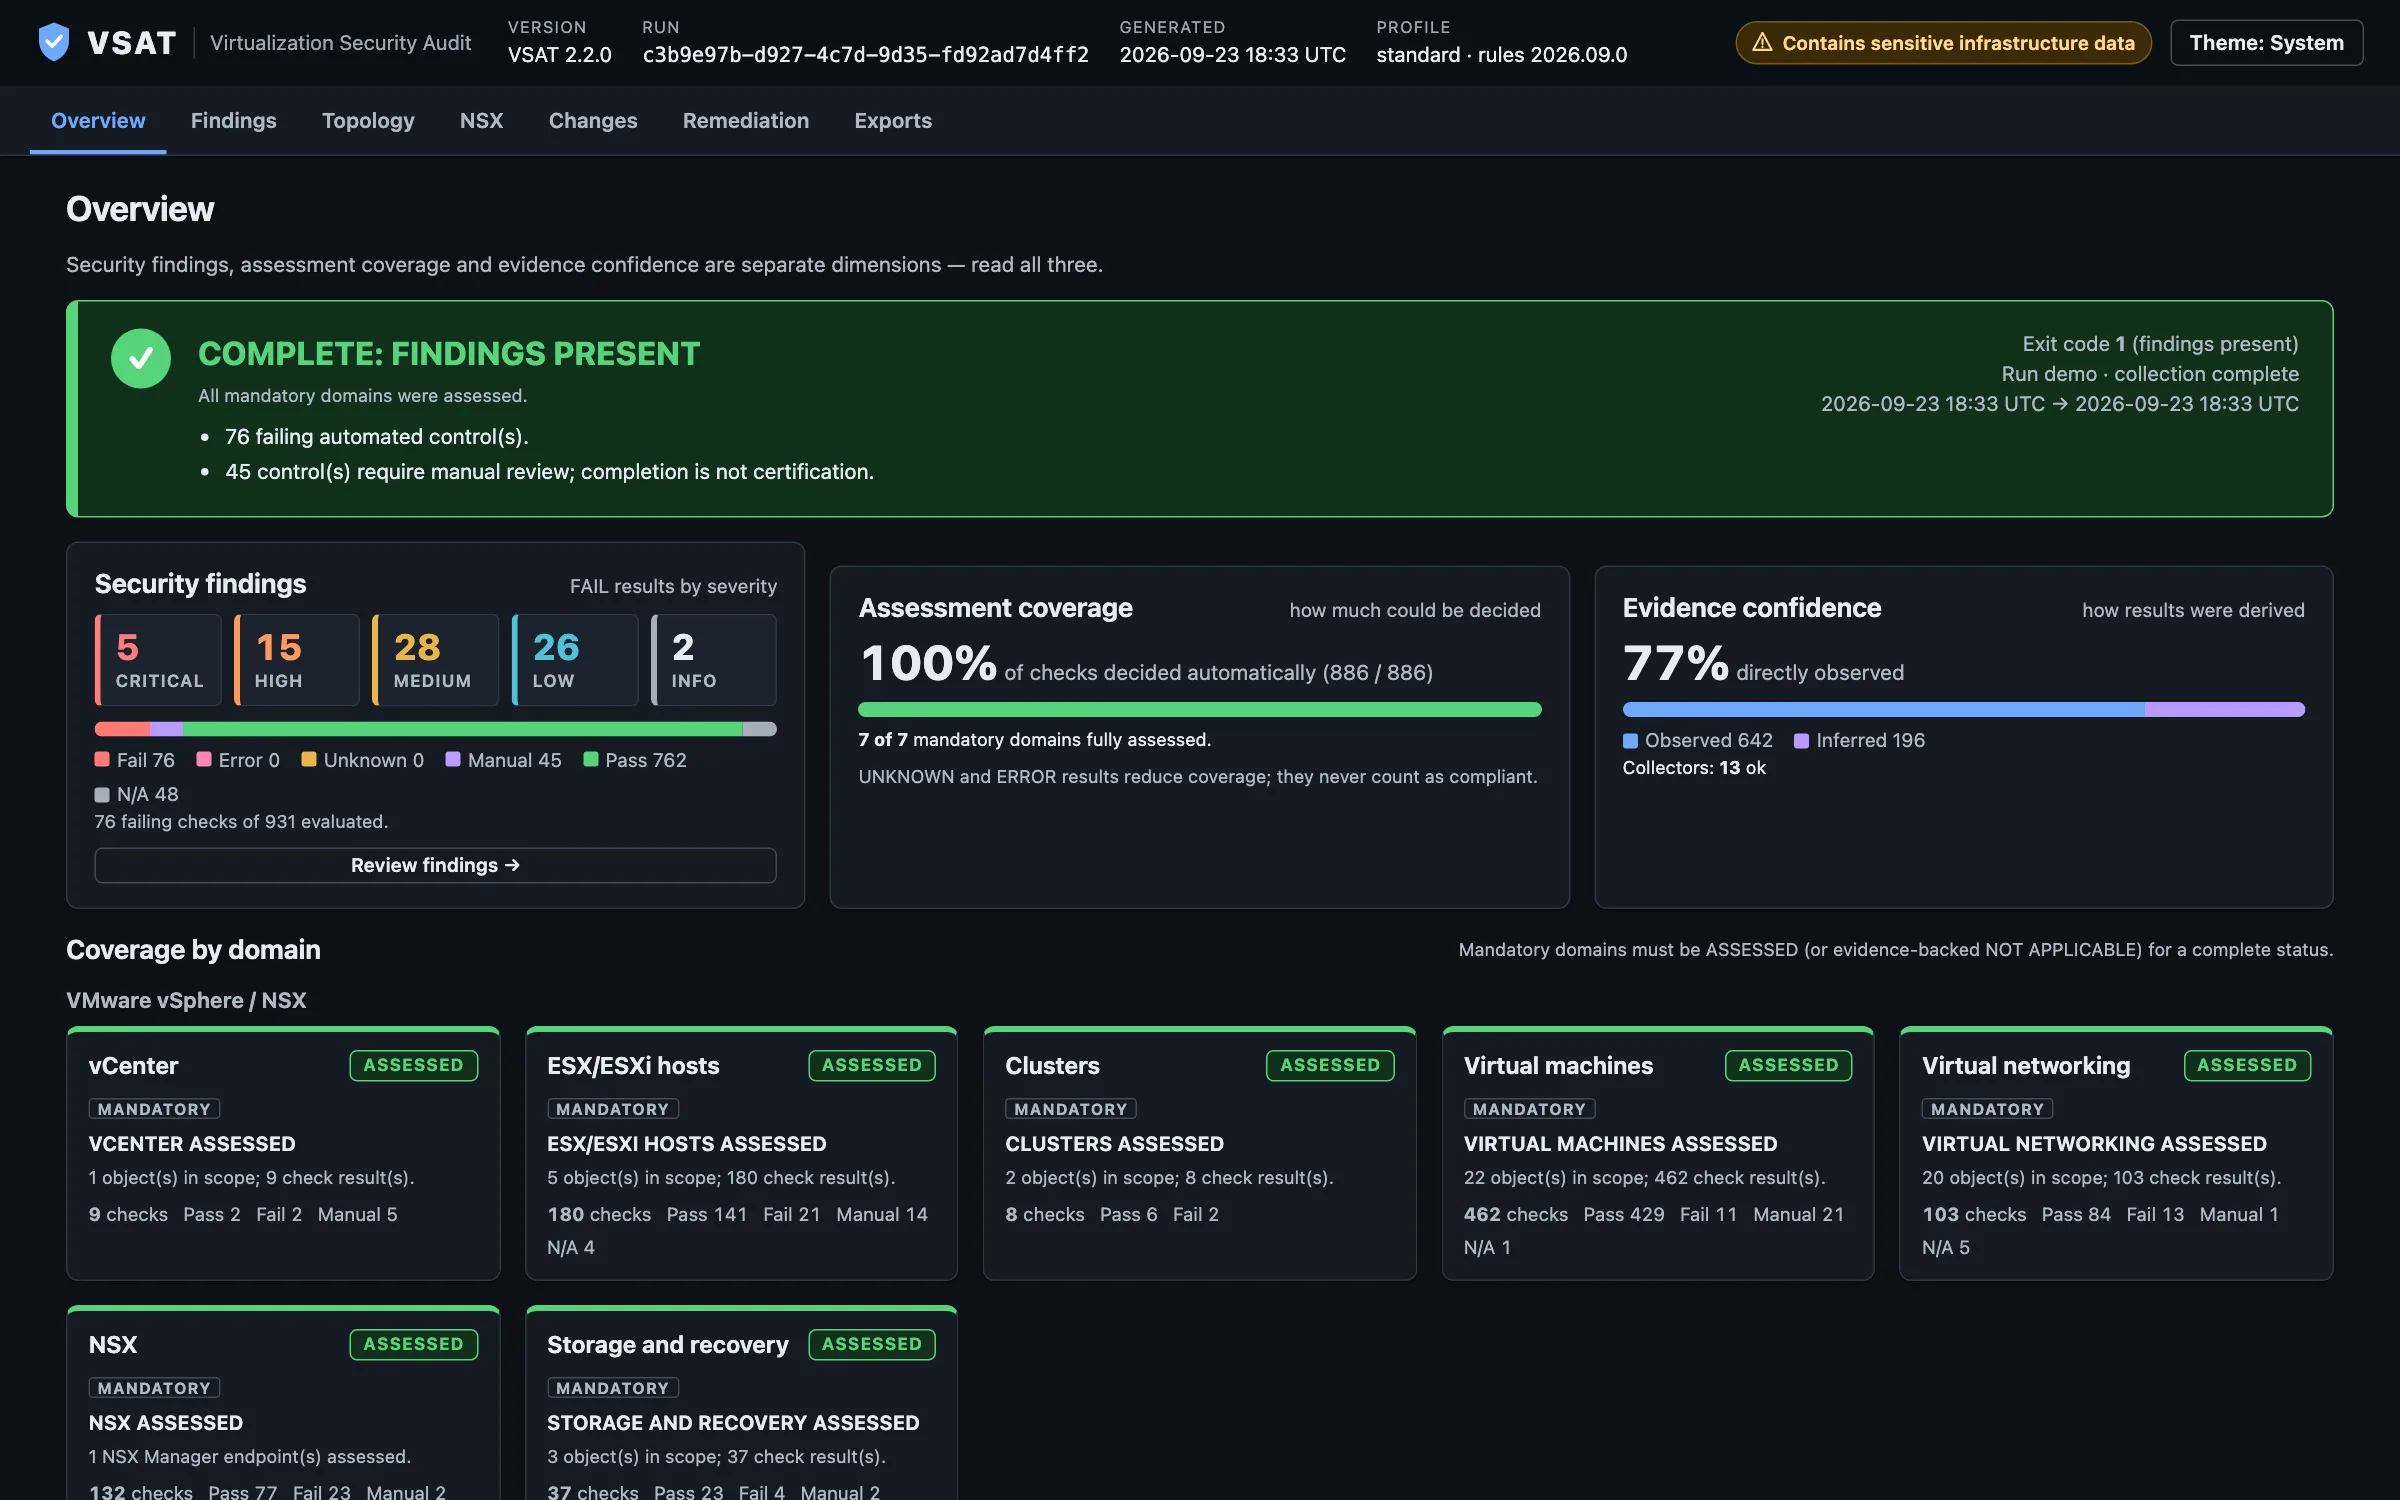
Report overview: status COMPLETE: FINDINGS PRESENT with exit code 1, failing checks by severity, 100 percent assessment coverage and 77 percent directly observed evidence, followed by coverage cards for each VMware domain.

What each feature is, and what it is not

Blast radius
Pick a compromised account or VM and see what an attacker reaches across every platform, and which fixes break the most paths.
Paths are inferred from configuration, with the confidence of each hop shown.
OT segmentation lens
Declare Purdue levels on scope zones and VSAT checks that OT and IT workloads do not share hosts, virtual switches, management planes, admin accounts or network paths.
Virtualization layer only. No OT network scanning, industrial protocols or field devices.
Ransomware readiness
Declare your backup systems and VSAT checks whether an attacker path reaches them, whether they run alongside production and whether production admins control them, plus how many hypervisors each account controls.
Backup software itself is not audited. Paths are inferred from configuration.
AI & GPU isolation
GPU passthrough and sharing, IOMMU, ACS overrides, SR-IOV next to management traffic, exposed model and dataset storage, and reachable Kubernetes control planes.
Reads configuration only; no GPU workload or model inspection.
Audit pack
One control matrix across NIST SP 800-53, IEC 62443-3-3, DISA STIG and ATT&CK mitigations, with your sign-offs and exceptions, the evidence package and its receipt. CIS through your own licensed benchmark.
Each mapping shows whether it has been reviewed. A satisfied control is not a certification.
MITRE ATT&CK mapping
Attack-path hops and rules map to ATT&CK techniques. Every run writes attack-layer.json for the ATT&CK Navigator.
Technique scores reflect configuration, not observed adversary activity.
Audit integrity
When the customer runs VSAT for you: the platforms' own change history for the engagement, earlier runs by the same account, -CollectOnly, and a receipt code read aloud that proves later the package is the one from that session.
History only goes back as far as the platforms keep logs. Short or cleared history is reported, never hidden.
Drift between runs
Pass -Baseline a previous evidence package to see new, resolved, changed and unassessed items, including asset and NSX rule changes.
Evidence that disappeared is shown as unassessed, never as resolved.
Explainable attack paths
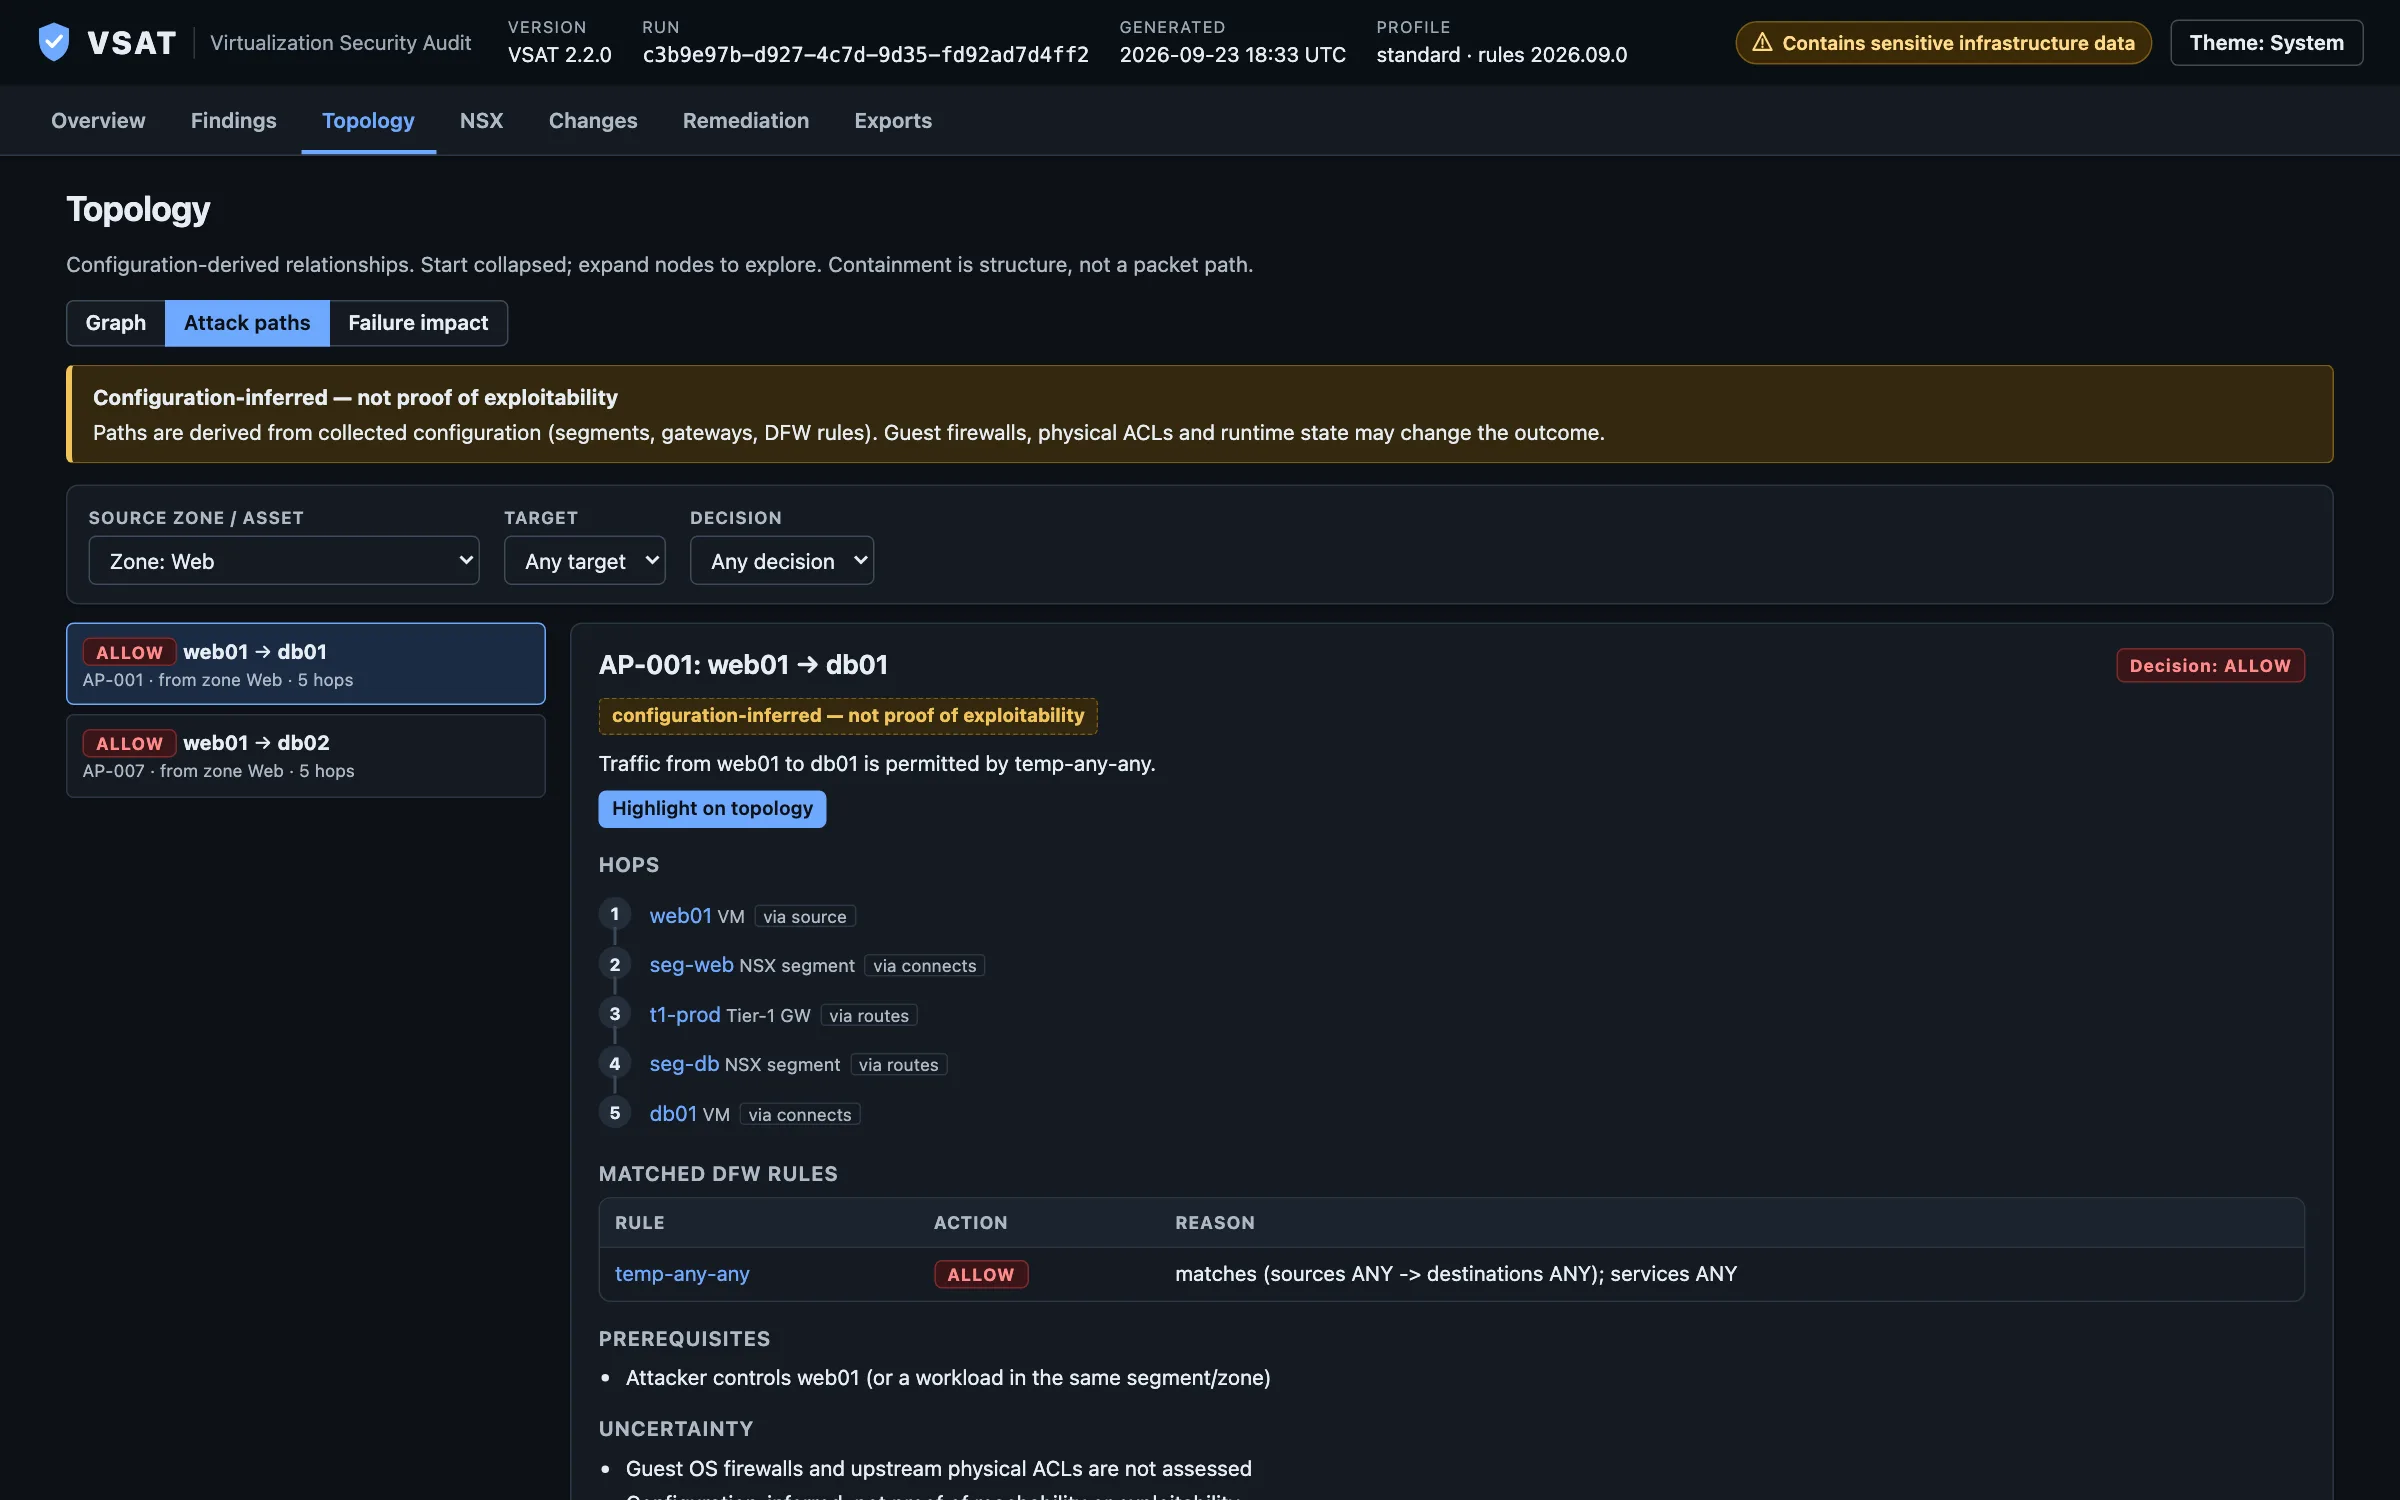
Paths inferred from segments, gateways and firewall rules, each explained rule by rule, plus privilege paths and chokepoint ranking.
Inferred from configuration. Not proof of reachability or exploitability.
Failure-impact explorer
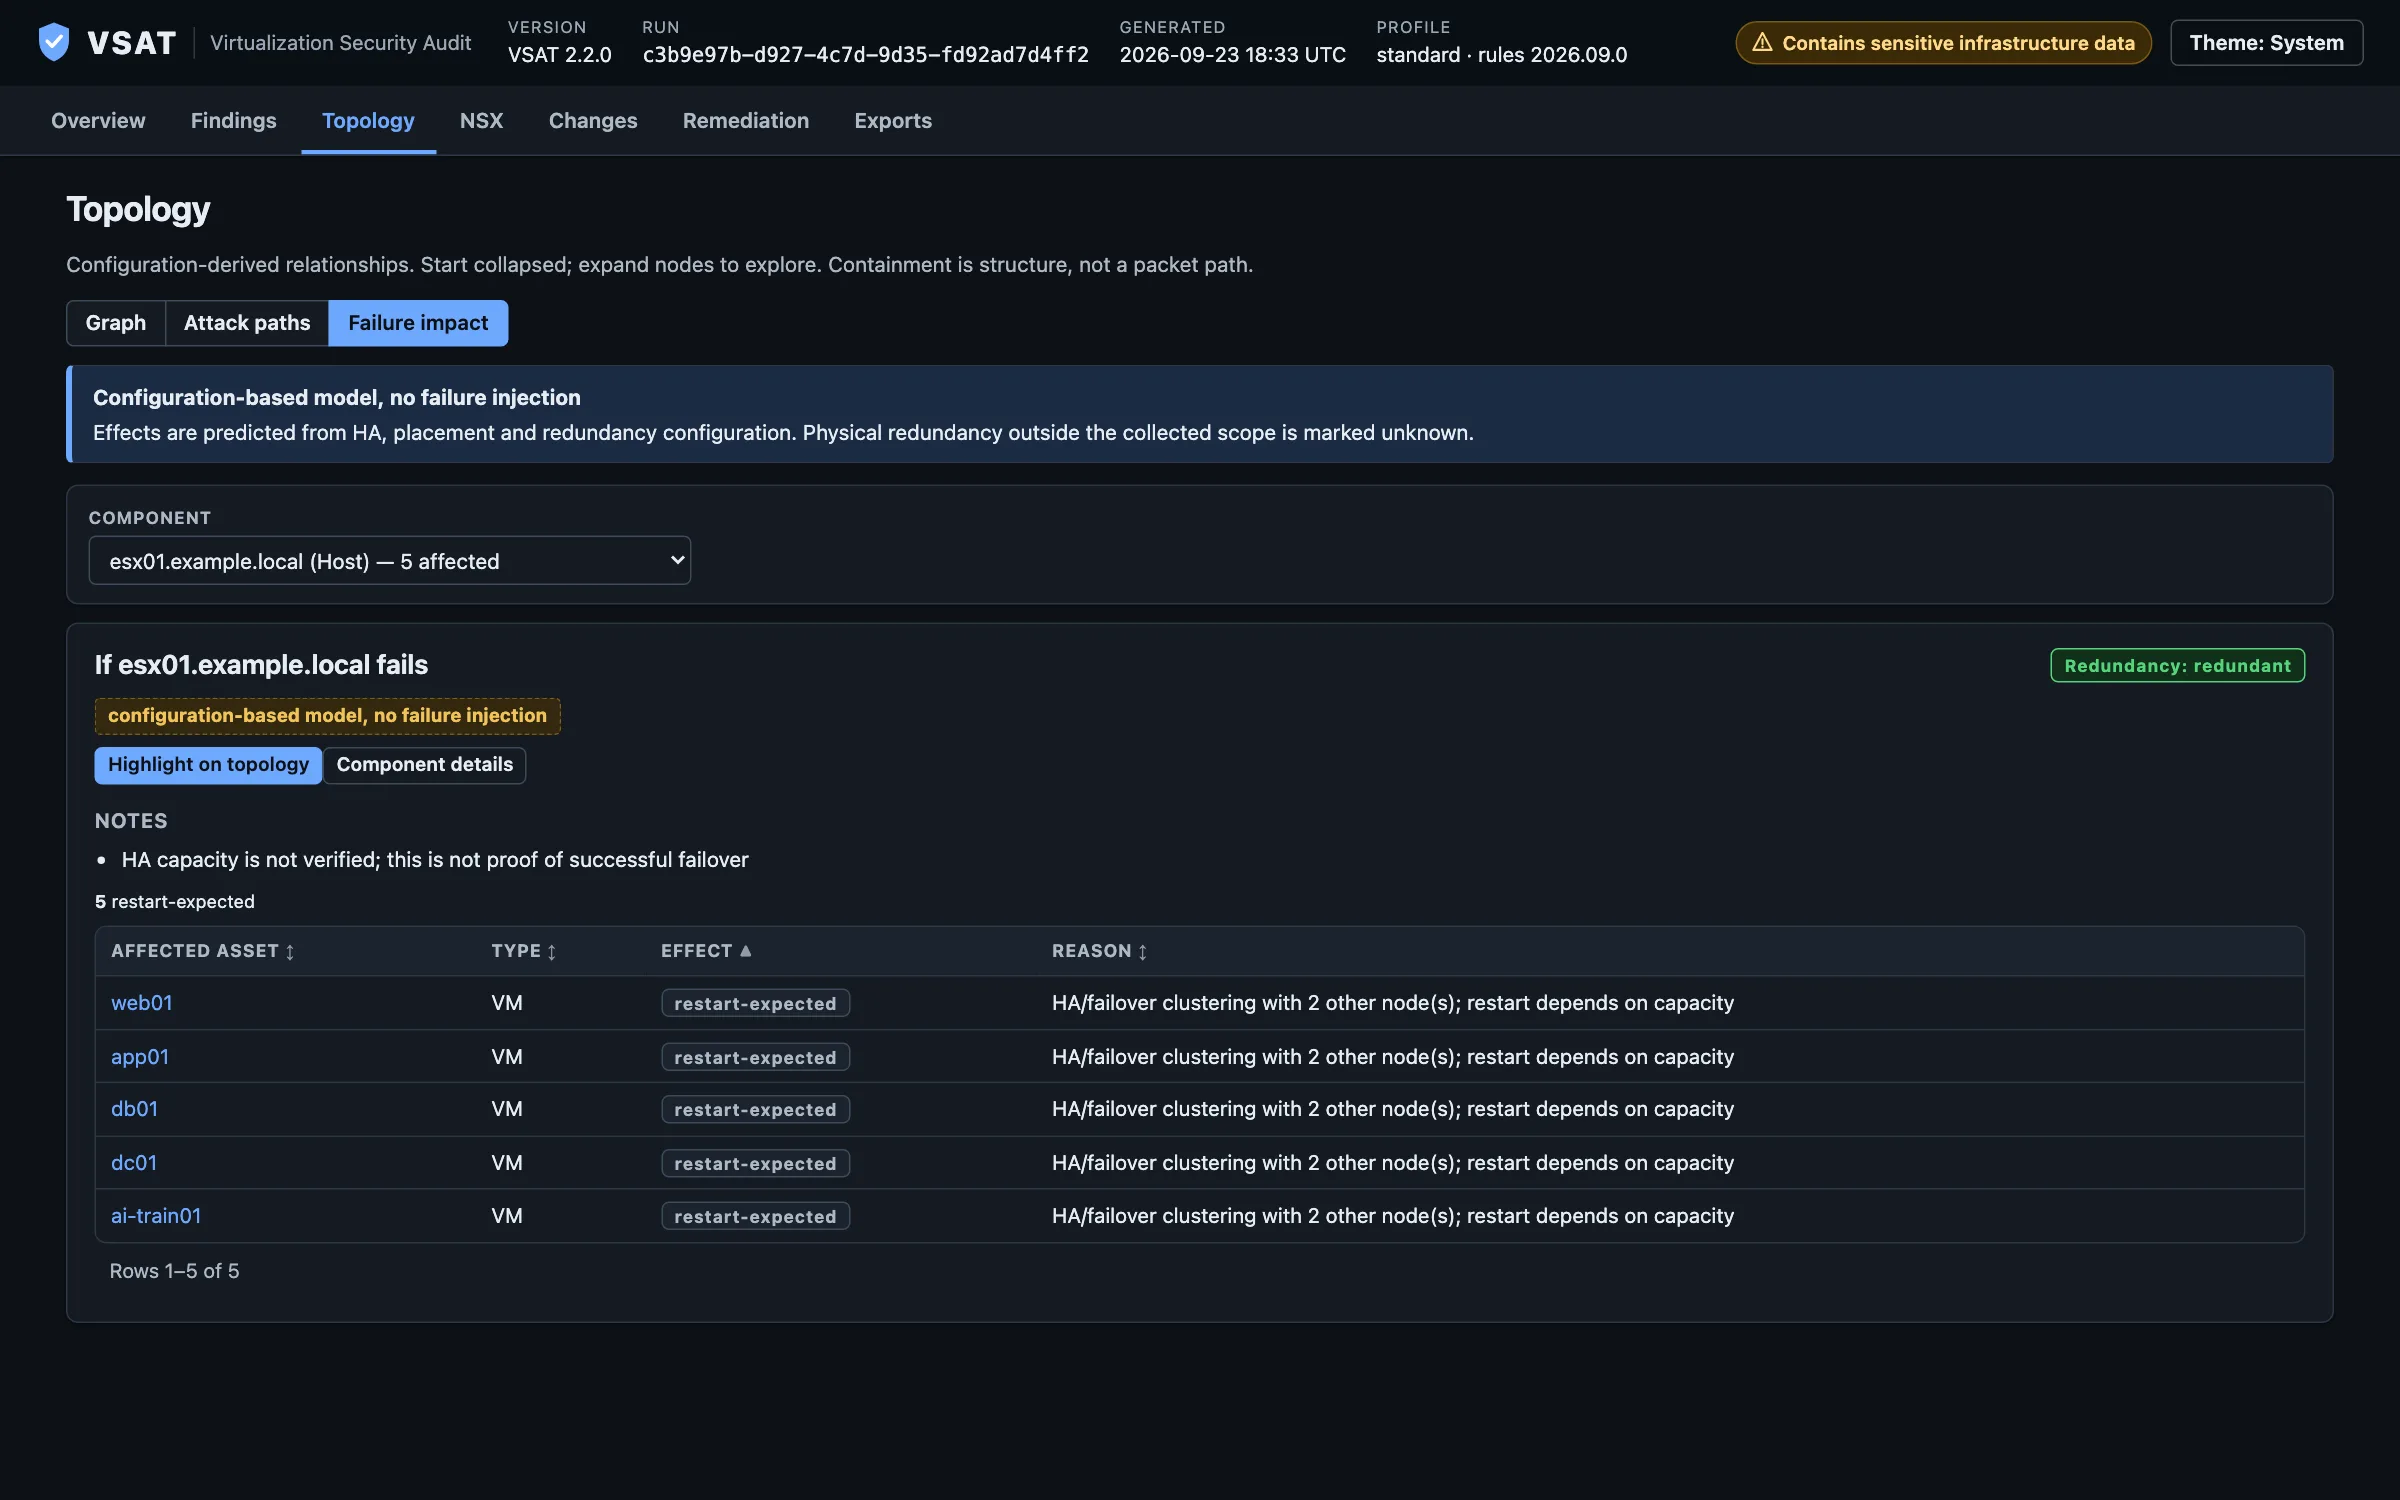
A dependency model of which workloads rely on a host, uplink, datastore, switch or NSX Edge.
A configuration model. VSAT injects no failures and does not prove failover.
Remediation work packages
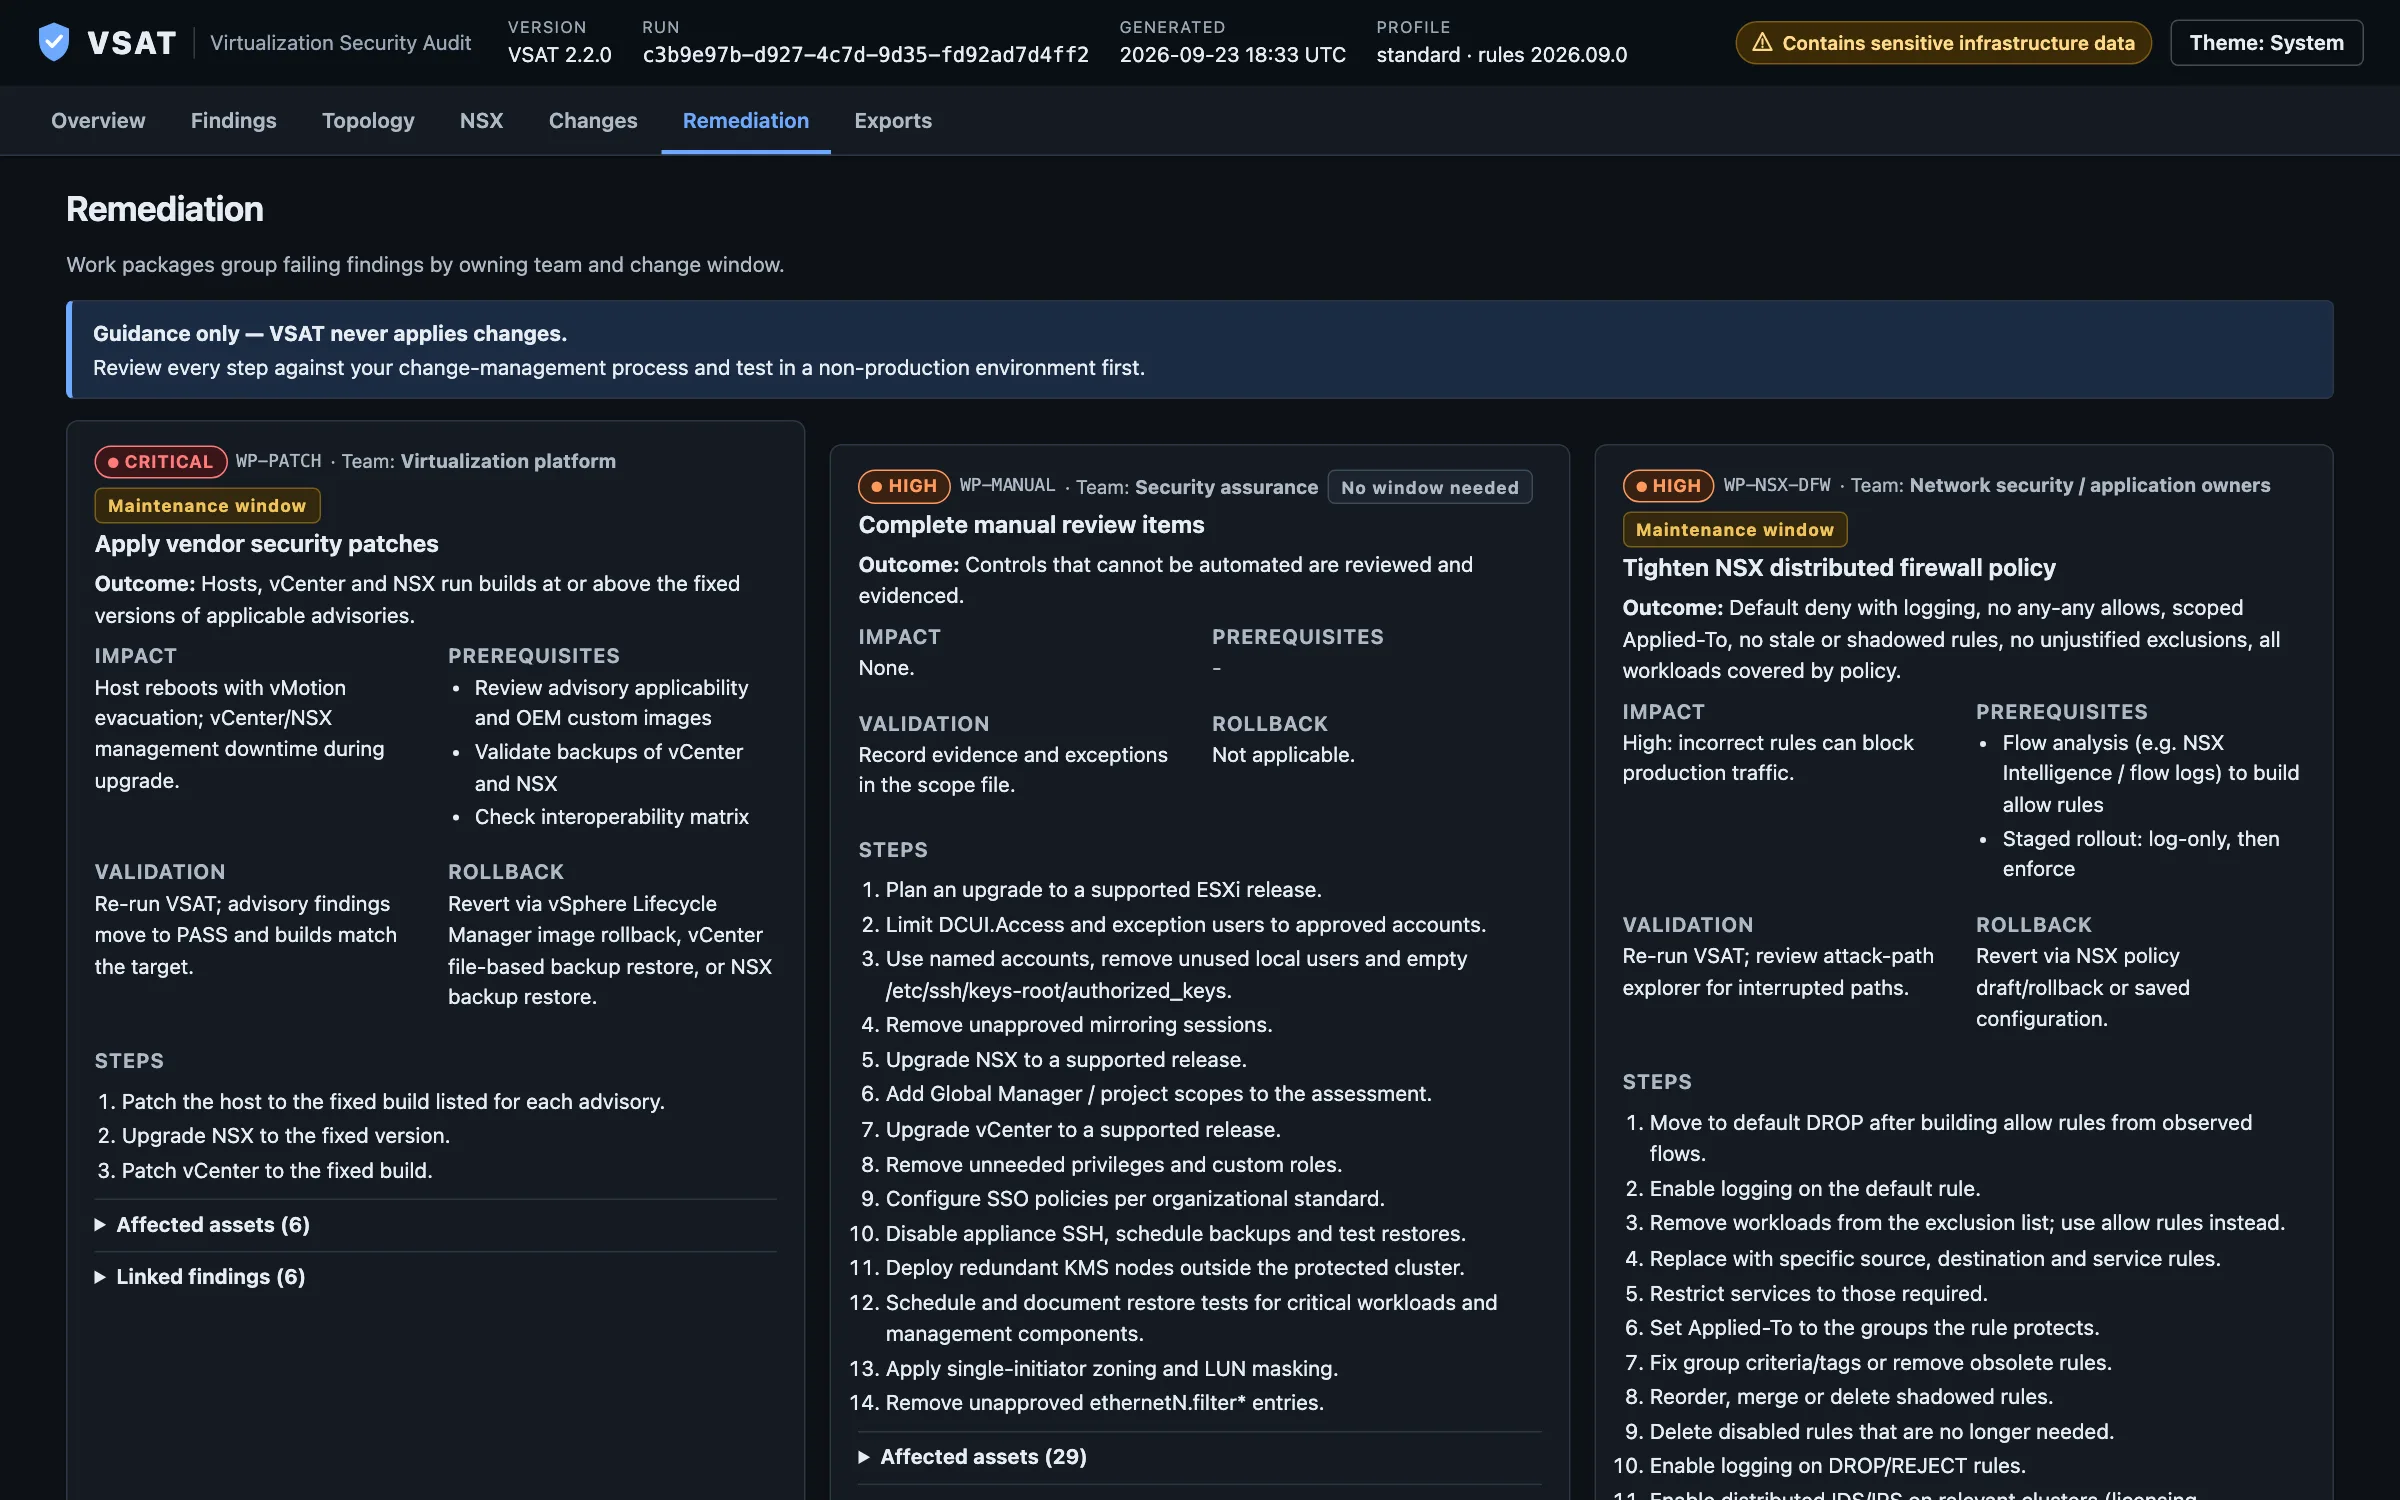
Corrective actions grouped by owning team, ready for ticketing through worklist.csv.
Guidance only. VSAT never applies a change.
Collect once, replay, share
-Replay re-evaluates a saved evidence package offline with no credentials. -Redact writes a sharing copy with consistent pseudonyms.
Evidence packages are hashed, not encrypted. Protect them with your own controls.
Unknown is not a pass.

Most audit scripts count what they could not read as fine. VSAT records how every fact was collected and keeps six result states apart, so a denied API call or an empty inventory never turns into a green check.

If NSX is detected but not assessed, the whole run reads INCOMPLETE: NSX NOT ASSESSED and exits with code 2.

  • PASSEvidence was collected and meets the expectation.
  • FAILEvidence was collected and does not.
  • MANUALNeeds human review. Completion is not certification.
  • NOT_APPLICABLEEvidence shows the object type is absent.
  • UNKNOWNEvidence was missing or denied. Lowers coverage, never raises a score.
  • ERRORCollection or evaluation failed, and says why.
Exit codes
0Complete, no failing automated controls
1Complete, with findings
2Incomplete or unknown mandatory coverage
3Fatal error
4Canceled

Three hypervisors, one evidence model

Each platform uses the same findings model, coverage rules, report and read-only guarantees. A domain VSAT could not read is reported as incomplete, not skipped.

VMware vSphere and NSX

Since 2.0.0127 rules

vCenter, ESXi hosts, clusters, virtual machines, virtual networking, NSX, storage and recovery

Read-only PowerCLI cmdlets for vSphere. NSX Policy and Manager REST calls pass an enforced allowlist: GET only, apart from session create and destroy.

-Server vc01 -NsxServer nsx01

Microsoft Hyper-V

Since 2.1.032 rules

Hyper-V hosts, virtual machines, virtual switches

One read-only collector over PowerShell remoting, or locally. Checks include VBS, HVCI and Credential Guard, Secure Boot and TPM, SMB signing, live migration, MAC spoofing and DHCP guard.

-HyperVServer hv01

KVM / libvirt

Since 2.2.023 rules

KVM hosts, guests, virtual networks

A read-only shell collector over SSH with key authentication and strict host-key checking; virsh always runs with --readonly. Checks include sVirt, unauthenticated libvirt TCP, QEMU as root, VNC TLS and nwfilter anti-spoofing.

-KvmServer kvm01

For hosts VSAT cannot reach, -ExportCollector hyperv or -ExportCollector kvm writes a standalone collection script. Run it on the host and import its output with -HyperVEvidence or -KvmEvidence.

Built for the air gap

No internet during an audit, report viewing or replay. No CDNs, web fonts, cloud accounts or telemetry. PowerCLI loads from the package's own ./modules folder, and every output is listed in a SHA-256 manifest.

Moving the offline package in

  1. On a connected machine, verify vsat.ps1 against SHA256SUMS.txt.
  2. Run build/New-OfflinePackage.ps1. It fetches pinned PowerShell and PowerCLI from vendor sources and checks their hashes.
  3. Record the ZIP hash and move it across on approved media.
  4. On the isolated runner, verify the hash, extract, and run .\VSAT.cmd.

PowerShell 7.4+ on Windows x64

# Guided browser UI on 127.0.0.1
.\vsat.ps1

# Synthetic lab, no connectivity
.\vsat.ps1 -Demo

# Terminal only, same mandatory domains
.\vsat.ps1 -Cli

# Hyper-V and KVM in the same run
.\vsat.ps1 -HyperVServer hv01 -KvmServer kvm01

# Air-gapped hosts: write a collector script
.\vsat.ps1 -ExportCollector kvm

# Customer runs it: collect only, read the receipt aloud
.\vsat.ps1 -CollectOnly -EngagementStart 2026-09-20
# Re-evaluate saved evidence and verify the receipt
.\vsat.ps1 -Replay .\assessment.vsat.zip -Receipt VSAT-XXXX-XXXX-XXXX-XXXX

Each run writes

  • report.htmlStandalone interactive report
  • assessment.vsat.zipEvidence package for replay and drift
  • findings.csvOne row per finding
  • worklist.csvWork packages for ticketing
  • changes.csvEngagement change timeline
  • audit-pack/Control matrix, sign-offs, exceptions (with -AuditPack)
  • attack-layer.jsonMITRE ATT&CK Navigator layer
  • manifest.jsonSHA-256 of every output and the receipt code

Built for credentials that matter

VSAT treats every inventory name, tag and imported file as untrusted, and assumes a hostile page may be open in the same browser.

Read-only by design
Read cmdlets for vSphere, a GET allowlist for NSX, Get-* and CIM reads for Hyper-V, and virsh --readonly for KVM.
Secrets stay in memory
Credentials are PSCredential objects, never accepted on the command line, never sent to the browser and redacted from logs.
Scoped trust
Pin a TLS thumbprint or SSH host key per endpoint with -TrustedThumbprint. Global PowerCLI certificate policy is never changed.
Hardened local UI
Loopback only, a random per-run token, Host and Origin validation, a CSRF header and no CORS.
Safe reports and imports
Strict CSP with hashes and safe DOM rendering. CSV formulas are neutralized. ZIP imports are size-limited and path-checked; collector XML is parsed without DTDs.
Residual risk, written down
PowerShell cannot guarantee secrets are wiped from memory, and loopback is not an authentication boundary. Read the threat model.

Current limits

What 2.7.0 does not cover. This list ships with every release.

  • Not a certification. VSAT is not certified by, endorsed by or affiliated with CIS, VMware, Broadcom or Microsoft. A clean run does not mean compliance.
  • Virtualization layer in OT. VSAT audits the hypervisors and virtual networks that host OT workloads. Field devices (PLCs, RTUs) and industrial protocols are out of scope.
  • Windows x64 runner. Linux and macOS are not supported runners.

Read the full list of limitations